mirror of
https://github.com/andwati/zitadel.git
synced 2026-10-18 05:52:51 +00:00


 cff4fe5dfd
# Which Problems Are Solved 1. Postgres spams FATAL: role "root" does not exist as mentioned in https://github.com/zitadel/zitadel/discussions/7832 (even with -U) 2. The compose commands for a ZITADEL deployment with initial service account key don't work out-of-the box with a non-root user, because docker creates non-existing directories to bind-mount with root ownership. 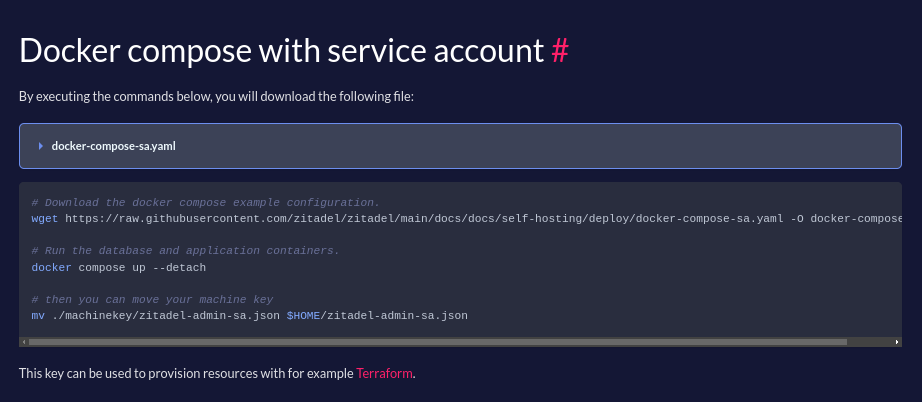 ``` time="2024-10-29T09:37:13Z" level=error msg="migration failed" caller="/home/runner/work/zitadel/zitadel/internal/migration/migration.go:68" error="open /machinekey/zitadel-admin-sa.json: permission denied" name=03_default_instance time="2024-10-29T09:37:13Z" level=fatal msg="migration failed" caller="/home/runner/work/zitadel/zitadel/cmd/setup/setup.go:248" error="open /machinekey/zitadel-admin-sa.json: permission denied" name=03_default_instance ``` # How the Problems Are Solved 1. The branch bases on https://github.com/zitadel/zitadel/pull/8826. The env vars are cleaned up and prettified across compose files. 2. A command is added to the docs that creates the directory with the current users permission. The ZITADEL container runs with the current users ID. # Additional Context - Replaces https://github.com/zitadel/zitadel/pull/8826 - Discussion https://github.com/zitadel/zitadel/discussions/7832 - Closes https://github.com/zitadel/zitadel/issues/7725 --------- Co-authored-by: m4tu4g <[email protected]>
50 lines
1.6 KiB
YAML
50 lines
1.6 KiB
YAML
services:
|
|
zitadel:
|
|
# The user should have the permission to write to ./machinekey
|
|
user: "${UID:-1000}"
|
|
restart: 'always'
|
|
networks:
|
|
- 'zitadel'
|
|
image: 'ghcr.io/zitadel/zitadel:latest'
|
|
command: 'start-from-init --masterkey "MasterkeyNeedsToHave32Characters" --tlsMode disabled'
|
|
environment:
|
|
ZITADEL_DATABASE_POSTGRES_HOST: db
|
|
ZITADEL_DATABASE_POSTGRES_PORT: 5432
|
|
ZITADEL_DATABASE_POSTGRES_DATABASE: zitadel
|
|
ZITADEL_DATABASE_POSTGRES_USER_USERNAME: zitadel
|
|
ZITADEL_DATABASE_POSTGRES_USER_PASSWORD: zitadel
|
|
ZITADEL_DATABASE_POSTGRES_USER_SSL_MODE: disable
|
|
ZITADEL_DATABASE_POSTGRES_ADMIN_USERNAME: postgres
|
|
ZITADEL_DATABASE_POSTGRES_ADMIN_PASSWORD: postgres
|
|
ZITADEL_DATABASE_POSTGRES_ADMIN_SSL_MODE: disable
|
|
ZITADEL_EXTERNALSECURE: false
|
|
ZITADEL_FIRSTINSTANCE_MACHINEKEYPATH: /machinekey/zitadel-admin-sa.json
|
|
ZITADEL_FIRSTINSTANCE_ORG_MACHINE_MACHINE_USERNAME: zitadel-admin-sa
|
|
ZITADEL_FIRSTINSTANCE_ORG_MACHINE_MACHINE_NAME: Admin
|
|
ZITADEL_FIRSTINSTANCE_ORG_MACHINE_MACHINEKEY_TYPE: 1
|
|
depends_on:
|
|
db:
|
|
condition: 'service_healthy'
|
|
ports:
|
|
- '8080:8080'
|
|
volumes:
|
|
- ./machinekey:/machinekey
|
|
|
|
db:
|
|
restart: 'always'
|
|
image: postgres:16-alpine
|
|
environment:
|
|
PGUSER: postgres
|
|
POSTGRES_PASSWORD: postgres
|
|
networks:
|
|
- 'zitadel'
|
|
healthcheck:
|
|
test: ["CMD-SHELL", "pg_isready", "-d", "zitadel", "-U", "postgres"]
|
|
interval: '10s'
|
|
timeout: '30s'
|
|
retries: 5
|
|
start_period: '20s'
|
|
|
|
networks:
|
|
zitadel:
|